
SECURITY HARDENING & PORTABILITY
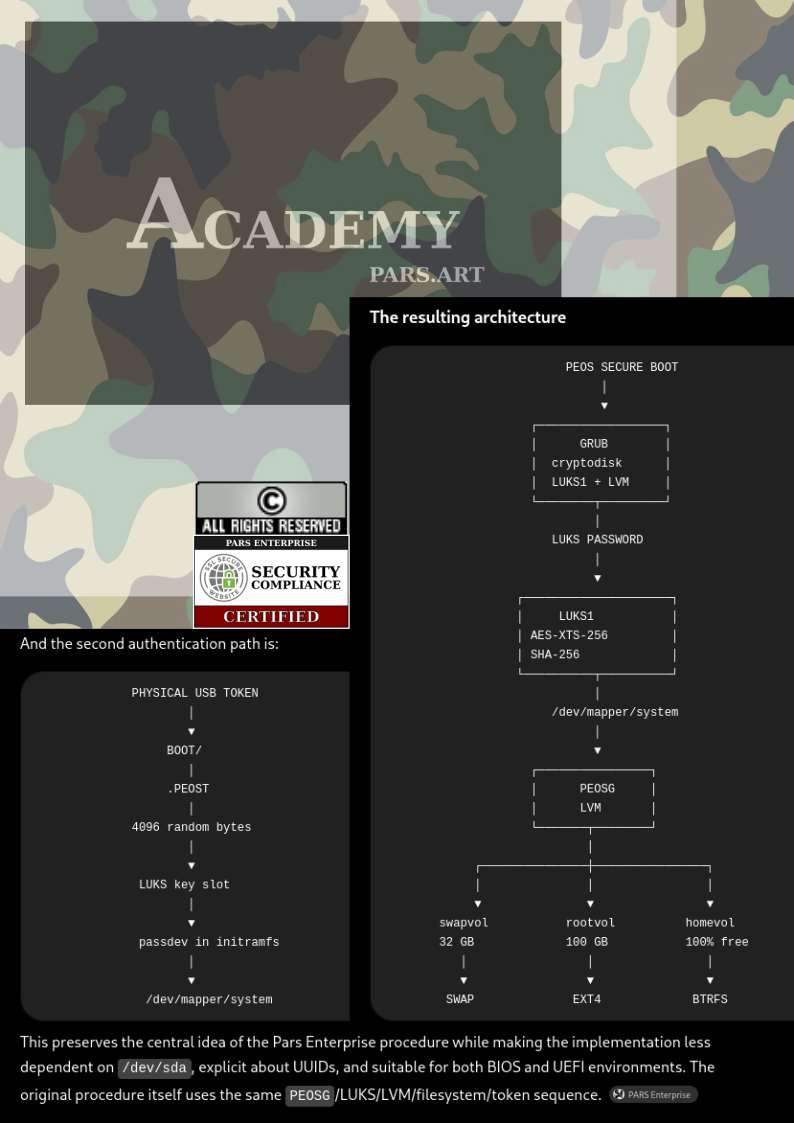
Preserve the central idea of the Pars Enterprise procedure while making the implementation less dependent on /dev/sda, explicit about UUIDs, and suitable for both BIOS and UEFI environments. The original procedure itself uses the same PEOSG/LUKS/LVM/ZFS/filesystem/token sequence.
SYSTEM BOOT ENCRYPTED!


Launched by the middle of 2015 with the purpose of hardening operating systems in field of information security and open-source software, one of our primary goals is to securing workstations including cloud services.
Plasma Desktop Wayland: https://parsenterprise.com/workstation
DIGITAL FORENSIC SUITE €0.00 EUR/ot
Page Term Reference
Comments